
TABLE OF CONTENT
Introduction
Ransomware no longer just locks files. Attackers now steal data before they encrypt it, then threaten to leak it if the ransom goes unpaid. The result is downtime, regulatory exposure and reputational damage, often at the same time.
What separates a contained event from a business crisis is rarely the strength of a single tool. It is how quickly and methodically an organization responds. This guide explains what ransomware incident response is, what it sets out to achieve, and how it works, phase by phase.
What is ransomware incident response?
Ransomware incident response (RIR) is the structured process an organization follows to detect, contain, investigate and recover from a ransomware attack. It brings together security operations, digital forensics, IT, legal, leadership and communications under one plan, so decisions are made fast and in the right order.
RIR is a specialized form of general incident response. Three things set it apart:
- Speed of spread. Ransomware moves laterally in minutes, so containment decisions cannot wait for a full picture.
- Double extortion. Most attacks involve data theft as well as encryption, which triggers breach-notification duties even if systems are restored.
- High-stakes decisions. Teams may face ransom negotiations, sanctions checks and law enforcement engagement, all under time pressure.
The NIST SP 800-61 Rev. 3 guidance, finalized in April 2025, frames incident response as part of wider cybersecurity risk management rather than a standalone activity. Effective RIR follows the same principle: it starts well before an attack and continues well after recovery.
Objectives of ransomware incident response
Every action in a ransomware response should serve one of six objectives:
- Contain the spread. Stop encryption and lateral movement before more systems are affected.
- Protect critical operations. Keep revenue-, safety- and customer-critical services running, or restore them first.
- Preserve evidence. Capture memory, disk images and logs before cleanup, so the root cause can be proven.
- Determine the full scope. Establish which systems were touched, which data was exfiltrated and how the attacker got in.
- Recover safely. Restore from clean, verified backups without reintroducing the attacker's persistence mechanisms.
- Meet legal duties and prevent recurrence. Notify regulators and affected parties on time, then close the gaps that allowed the attack.
These objectives sometimes pull against each other. Powering a server down, for example, stops encryption but destroys volatile memory evidence. A tested plan settles these trade-offs in advance, so responders are not debating them mid-incident.
How ransomware incident response works
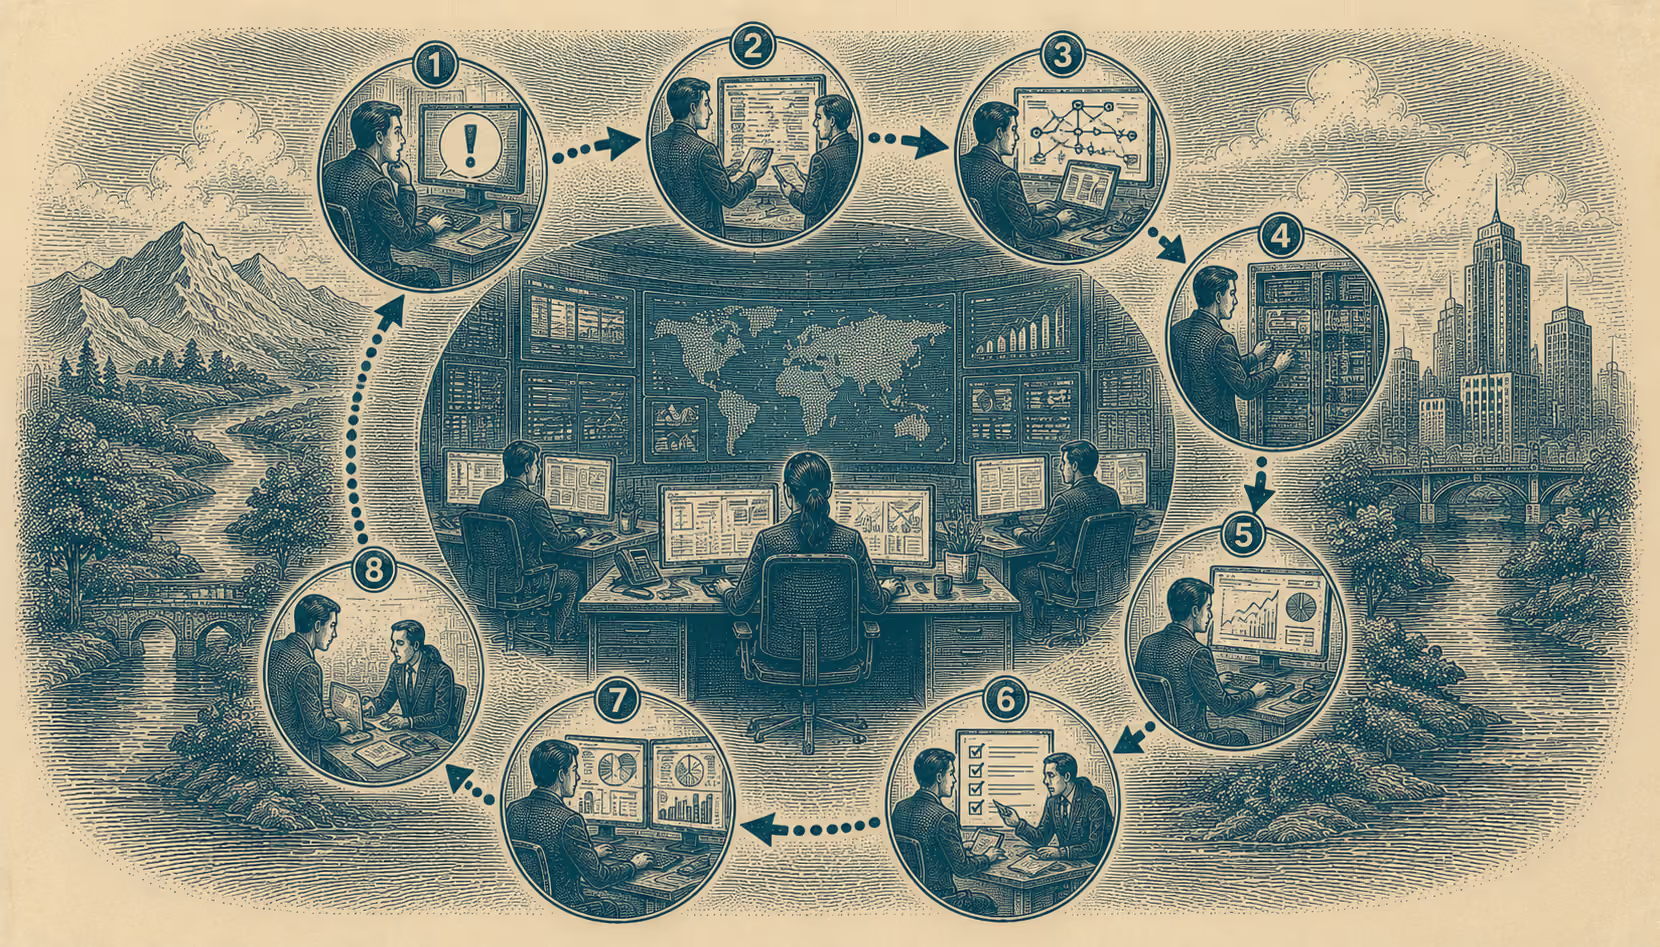
Ransomware incident response runs in five phases. In practice they overlap: investigation continues during containment, and hardening starts during recovery.
1. Preparation
Response capability is built before an attack. Define roles, escalation paths and communication protocols in a ransomware-specific plan. Keep offline or immutable backups and test restoration at least quarterly. Rehearse the plan with tabletop exercises and an adversary-led ransomware simulation, and agree external support in advance through a DFIR retainer.
2. Detection and analysis
Early signs include mass file renaming, ransom notes, spikes in EDR alerts, unusual outbound traffic and precursor malware. Continuous monitoring through an agentic SOC shortens the gap between first foothold and first alert. Once confirmed, activate the response team, start an evidence log, identify the ransomware variant, and check whether data was exfiltrated before encryption.
3. Containment
Isolate affected systems by disconnecting them from the network rather than powering them off where possible, so memory evidence survives. Disable non-essential privileged accounts, reset credentials and protect known-good domain controllers. Before any cleanup, capture disk images, memory and logs from a sample of affected hosts.
4. Eradication and recovery
Remove the ransomware, its persistence mechanisms and the access path the attacker used. A ransomware event is often the final stage of a longer intrusion, so a compromise assessment helps confirm the environment is clean. Then restore from verified backups in order of business priority, patch and harden before reconnecting, and watch restored systems closely for reinfection.
5. Post-incident activity
Run a lessons-learned review and update the plan. Close the gaps the attacker exploited through segmentation, MFA on privileged access and regular network penetration testing. Meet notification duties under regulations such as GDPR and India's DPDP Act, and keep internal and external messaging consistent.
Common ransomware response mistakes
Forensic investigations repeatedly surface the same avoidable errors:
- Wiping before imaging. Rebuilding systems first destroys the evidence needed to find the entry point.
- Restoring too early. Backups restored into an environment the attacker still controls are re-encrypted within days.
- Ignoring exfiltration. Treating the incident as an availability problem only can mean missed notification deadlines.
- Leadership learning on the day. Executives who have never rehearsed a crisis management exercise slow down every decision.
Most of these mistakes are settled long before an attack, through a ransomware prevention program and a plan that has actually been tested.
How SISA helps with ransomware incident response
SISA's Digital Forensics & Incident Response (DFIR) teams have deep expertise in breach investigations, and that forensic experience shapes every engagement. Our ransomware incident response service combines rapid containment, root-cause forensics and guided recovery, with cloud forensics for hybrid and multi-cloud environments. Findings from these investigations feed our Digital Threat Report 2025-26 – that delves deep into evolving cyber threat landscape in the BFSI sector, emerging attack patterns and recommended security measures for the payments ecosystem.
Before an attack, we help you test readiness through breach and attack simulation and retainer-backed response planning.
Experiencing an attack now? Call SISA's breach hotline on 1800 203 6701 or contact our DFIR team.
Frequently asked questions
1. What is the first step in ransomware incident response?
Isolate affected systems from the network to stop the spread, ideally by disconnecting them rather than shutting them down. Then activate your response team and start documenting everything you observe.
2. What are the main objectives of ransomware incident response?
To contain the attack, protect critical operations, preserve evidence, determine the full scope, recover safely, and meet legal obligations while preventing recurrence.
3. Should you pay the ransom?
Government agencies and most security experts advise against it. Payment does not guarantee decryption or deletion of stolen data, and it funds further attacks. Any such decision should involve legal counsel and specialist advisors.
4. How is ransomware incident response different from general incident response?
It deals with faster lateral spread, likely data exfiltration, and decisions on ransom, sanctions and law enforcement, so it needs its own playbook within the wider incident response plan.
5. How often should backups be tested?
At least quarterly, and after any major infrastructure change. Keep offline or immutable copies so attackers cannot encrypt them.