
TABLE OF CONTENT
In 2026, the velocity and complexity of cyber attacks have shattered traditional security paradigms. Leveraging autonomous AI and polymorphic malware, threat actors frequently deploy "fileless" malware and "Living off the Land" (LotL) techniques specifically designed to bypass static, signature-based perimeter defenses. Once inside, adversaries operate stealthily, dwelling in networks while legacy tools remain blind.
Historically, cyber threat hunting was a highly manual, resource-intensive exercise. An analyst might spend up to 40 hours executing a single manual hunt—sifting through complex log queries, building hypotheses, and correlating data across disparate tools. Today, security teams lack the time and staffing to operate at that pace; in fact, over 60% of organizations cite personnel shortages as their primary barrier to threat hunting.
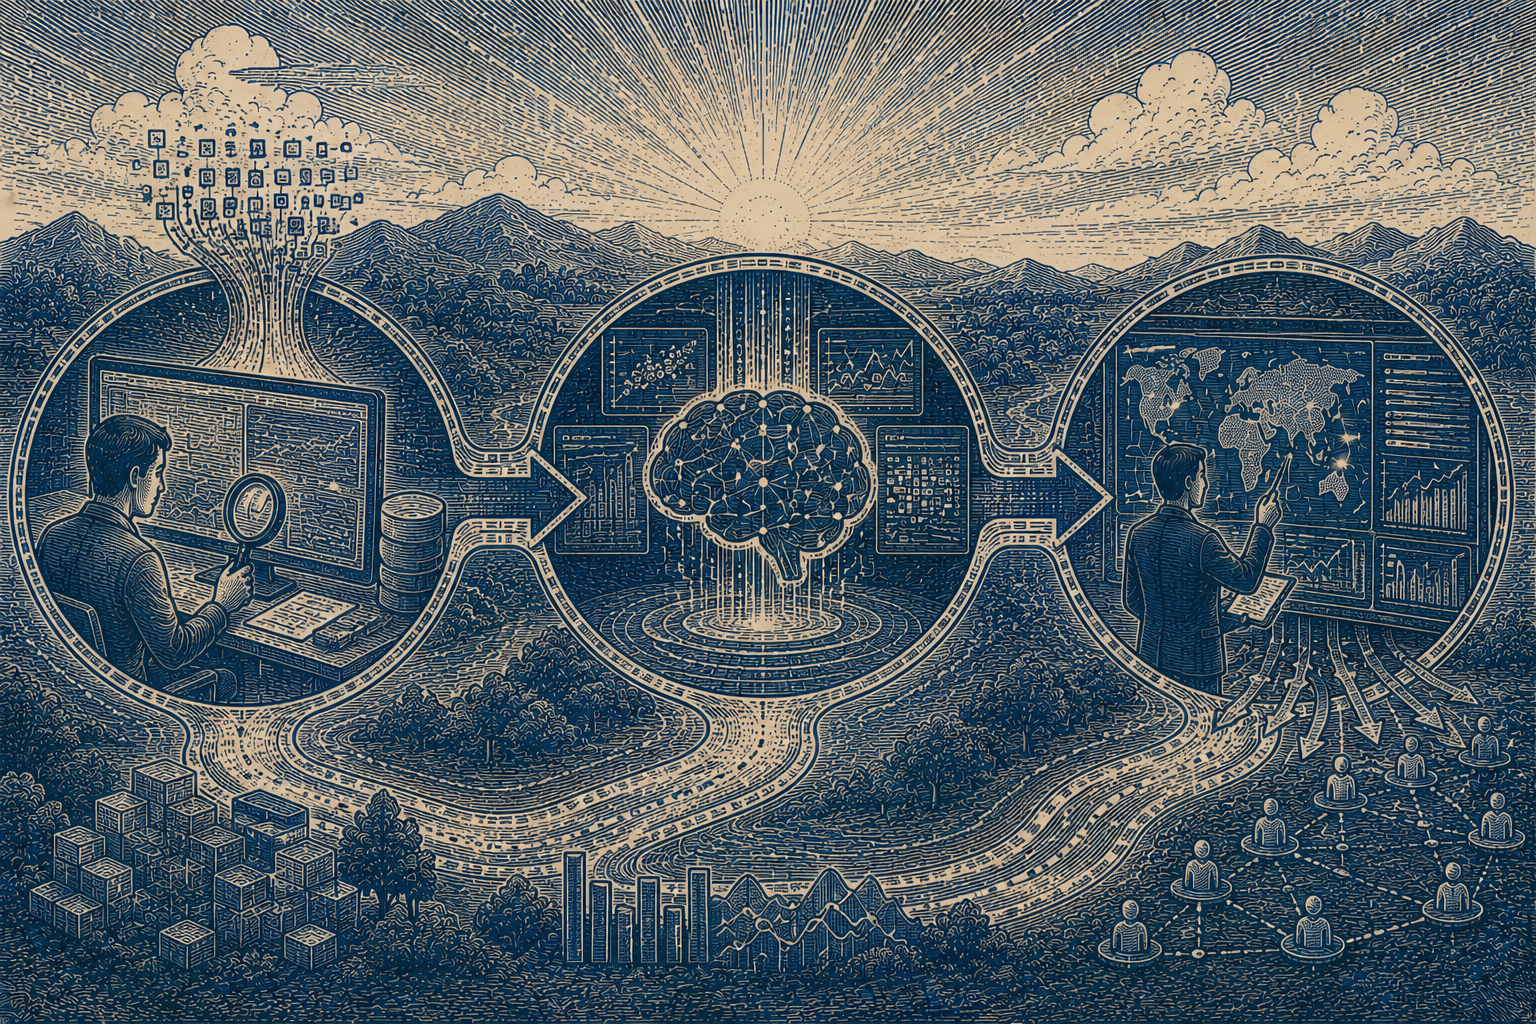
The strategic solution is integrating Machine Learning (ML) into the threat-hunting pipeline. ML models analyze telemetry at machine speed, shifting hunting from a periodic manual exercise to a continuous, 24/7 proactive defense. Here is the definitive 3-step guide to executing ML-driven cyber threat hunting in 2026.
Step 1: Telemetry Aggregation and Feature Engineering
The effectiveness of any machine learning algorithm is strictly bound by the quality of the data it consumes. You cannot hunt effectively in siloed environments.
- Comprehensive Data Ingestion: ML threat-hunting models require a unified data pipeline that ingests high-fidelity telemetry across the entire IT estate. This includes endpoint telemetry (EDR), authentication logs, network traffic, and cloud infrastructure logs (e.g., AWS CloudTrail, Azure Sentinel).
- Feature Engineering: Raw log data is largely unintelligible to ML models without context. Feature engineering transforms raw data into mathematical vectors that represent user and system behavior. Key engineered features include login frequencies, session duration anomalies, burst login attempts, and off-hours access. Proper feature engineering is often far more critical to hunting success than the specific ML algorithm chosen.
Step 2: Anomaly Detection via Unsupervised Learning
Once the data is normalized and structured, the ML models are deployed to isolate threats. In modern threat hunting, Unsupervised Learning is the core operational engine. Unlike supervised learning, which relies on labeled data of known attacks, unsupervised learning excels at discovering zero-day anomalies and stealthy insider threats without prior context.
- Establishing Behavioral Baselines: Algorithms such as Isolation Forests, K-Means Clustering, and Autoencoders establish a baseline of "normal" behavior for every user, device, and application in the network.
- User and Entity Behavior Analytics (UEBA): Powered by ML, UEBA continuously monitors the environment in real time. If an authenticated user suddenly executes irregular PowerShell scripts or attempts unauthorized lateral movement, the algorithm instantly flags the deviation.
- Scoring and Prioritization: Instead of flooding the SOC with low-level alerts, ML algorithms assign dynamic anomaly scores to events. This allows the system to isolate rare patterns and surface only high-risk anomalies, drastically reducing false positives and analyst alert fatigue.
Step 3: Human-in-the-Loop Investigation and Automated Response
Machine learning acts as a profound force multiplier, but it does not completely replace human expertise. ML highlights what is anomalous; human analysts determine if the anomaly is genuinely malicious.
- Hypothesis Validation: Elite threat hunters take the high-risk anomalies flagged by the ML models and correlate them with global threat intelligence, IP reputation, and frameworks like MITRE ATT&CK.
- Agentic SOC Orchestration: In mature 2026 environments, this human-in-the-loop investigation is augmented by automation. Platforms like the SISA ProACT Agentic SOC deploy autonomous AI agents to instantly trace the blast radius of an anomaly across identity, network, and endpoint layers, performing initial correlation at machine speed.
- Forensics-Driven Containment: Once a threat is validated, immediate digital forensics and incident response (DFIR) protocols are executed. Partnering with a Managed Detection and Response (MDR) provider ensures that compromised assets are instantly isolated and the threat is eradicated before data exfiltration can occur.
Why ML is Mandatory for Modern Threat Hunting
- Defeating Fileless Malware: ML models trained on behavioral baselines catch malicious hands-on-keyboard activities, abnormal authentication sequences, and data staging behaviors that signature-based systems miss entirely.
- Scaling Without Headcount: By automating the search and data-correlation phases, existing security teams can run continuous, parallel hunts across vast data lakes without requiring additional personnel.
- Continuous Defense: Rather than relying on reactive monthly hunts, ML-augmented systems test threat hypotheses around the clock, continuously closing the gap between compromise and detection.
To continuously validate the efficacy of your ML-driven hunting program, organizations should regularly test their analytical models using automated Breach and Attack Simulation (BAS), ensuring the algorithms correctly identify simulated adversarial movement under live conditions.
FAQs
Q1: What is the difference between signature-based detection and ML threat hunting?
Signature-based systems rely on known hashes and rules to block previously identified malware. ML threat hunting utilizes behavioral baselines to identify anomalies and zero-day techniques that have never been seen before, capturing evasive "fileless" attacks that signatures miss.
Q2: What role does UEBA play in threat hunting?
User and Entity Behavior Analytics (UEBA) leverages unsupervised machine learning to baseline standard behavior across the network. It detects subtle insider threats, credential misuse, and lateral movement by flagging deviations in real time.
Q3: Can Machine Learning completely replace human threat hunters?
No. The industry best practice dictates a "human-in-the-loop" model. Machine learning excels at processing massive datasets and highlighting suspicious anomalies at scale, but skilled human analysts are required to provide contextual validation and determine if the activity is a genuine threat.
Q4: Why is Feature Engineering important in the ML pipeline?
Machine learning algorithms cannot effectively interpret raw, unstructured logs. Feature engineering transforms raw data into specific, measurable indicators (such as off-hours login attempts or burst traffic) so the algorithms can accurately detect behavioral deviations.
Q5: What are the best tools for executing ML threat hunts?
Effective threat hunting requires robust infrastructure. Security teams rely on cyber threat hunting tools such as advanced SIEM platforms (e.g., Splunk ML Toolkit), Endpoint Detection and Response (EDR) telemetry, and dedicated ML-driven Agentic SOC platforms that integrate seamlessly with SOAR workflows.